 Chiho AI
What Is a Telegram MCP Server? The Main Architectures Explained
A Telegram MCP server connects an AI application to Telegram-related tools through the Model Context Protocol. That name does not tell you which Telegram identity it uses or what it can access. In practice, projects use it for three different jobs: working with an account's conversations, testing a Telegram bot, or using Telegram to communicate with an agent running elsewhere.
Choose the job before choosing a server. A bot-testing adapter will not necessarily supply your team's customer history, and a phone-based agent remote does not automatically become a Telegram CRM.
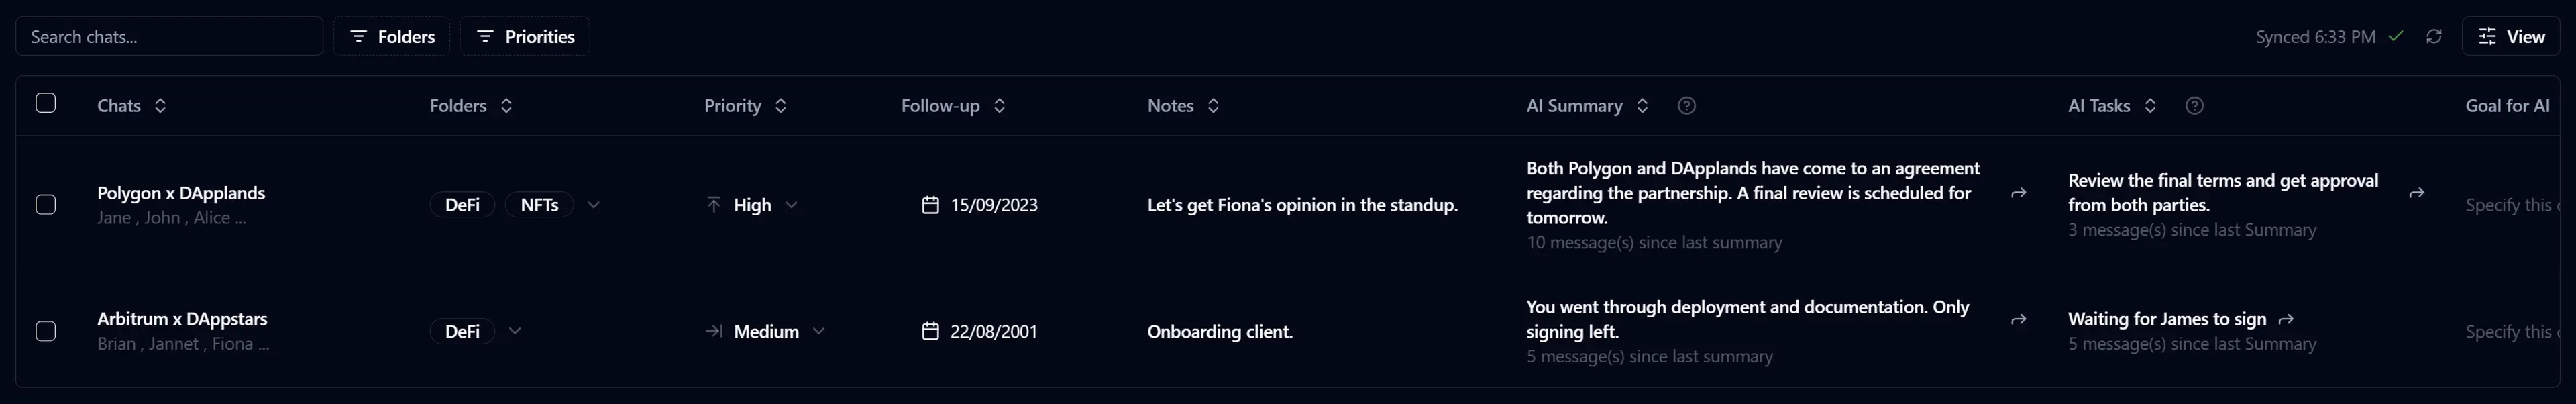
Header image: an existing Chiho CRM interface image; not an MCP test result.
Publisher disclosure: Chiho publishes this guide and provides a hosted Telegram MCP service. The examples below illustrate documented architectures, not a ranking or a hands-on comparison. Documentation and Chiho source were reviewed on 23 September 2026; no competitor runtime or live customer-account experiment was performed.
What MCP supplies—and what the Telegram adapter decides
MCP defines how an AI application connects to a server and discovers capabilities such as tools. Servers can run locally or remotely. The protocol itself does not decide which Telegram account is connected, which messages are available, or whether sending needs approval. Those are implementation and configuration questions. See the MCP architecture documentation.
Separate three decisions:
- Purpose: read customer conversations, test a bot, or communicate with an agent.
- Telegram identity: a connected user account, a bot identity, or a browser session used by a tester.
- Operating model: a hosted service or a runtime you operate yourself.
These dimensions can overlap. A local server can access a user account; a hosted service can do the same. A product can expose several modes. The word “remote” may describe an HTTP endpoint or controlling an agent from your phone—ask which meaning applies.
Architecture 1: an agent works with Telegram account data
Here the AI client asks an MCP server to retrieve information from a connected Telegram account. The server may also expose actions and CRM context. The useful question is whether it can retrieve the particular conversations and message range your task needs, under the intended account and workspace permissions.
For a sales handover, for example, an agent might read a permitted customer conversation and identify the last confirmed commitment. That requires access to the conversation and enough history to support the answer. A list of tool names or a successful login does not prove either condition.
Chiho's Telegram agent repository documents two account-access paths: hosted Chiho MCP with browser OAuth, and the self-hosted tgchats local runtime over stdio using the operator's Telegram credentials and storage. They are separate packages and operating models. The hosted service also connects to Chiho's CRM workflows; do not assume every local and hosted feature has identical behavior.
For the hosted connection, use the maintained Chiho Telegram MCP page. Its consent flow grants the current Telegram and CRM capabilities, including available writes; choosing a read-only first task does not make the underlying grant read-only. Chiho requires stored previews and approval for member invitations and group exits, and can require approval for batch sends. Other writes can execute directly after any client-side control. Check the particular tool and client settings rather than assuming all writes pause for review.
Account access also differs from CRM coverage. A live conversation may not yet have a persisted CRM row, and a partial history read cannot establish that an older commitment never existed. Our guide to Telegram chat counts explains the inventory distinction.
Architecture 2: an agent tests a Telegram bot as a user
A bot developer may want an agent to inspect a welcome screen, follow buttons, or check a Mini App. This is a user-interface testing problem, even though the target is a bot.
For example, telegram-bot-testing-mcp documents an adapter that drives the official Telegram Web client in a browser. Its exposed operations include reading messages, pressing buttons, sending files, and inspecting Mini Apps. Its README recommends a dedicated test account and treats the browser profile as sensitive session material. These are documented capabilities, not results we independently reproduced.
The identity distinction matters: the bot is the target being tested, while the adapter uses a logged-in user session. “Bot testing” does not mean the adapter authenticates using your bot's token.
An illustrative test might check whether a support bot displays the expected menu after a command. Sending that command or pressing a button can change state. Start by reading existing test output; run interaction scenarios only in an authorized test environment with known effects. A test environment label alone is not evidence that real customers or payments are unreachable.
This architecture fits bot regression work. It does not, by itself, establish team ownership, CRM persistence, or access to all customer conversations.
Architecture 3: Telegram is the remote interface to an agent
In this arrangement, you use Telegram to exchange instructions or status with an agent running on another machine. The desired outcome is supervising the agent, rather than searching a customer account.
The mcp-telegram-claudecode repository documents sending and receiving messages between Claude Code and Telegram, with a bot token and configured chat ID. It also describes remote permission decisions through hooks. This illustrates the control-channel pattern; it is not a security endorsement or a verification that those controls fit your environment.
For example, an operator might receive a build-status message on their phone. That says nothing about whether the agent can read an unrelated customer conversation. Conversely, a customer-history connector does not necessarily provide a phone-based approval interface.
Evaluate who may issue commands through the channel, what the agent can do on its host, and how an approval identifies the exact action. A message appearing in Telegram is not enough to establish trustworthy authorization.
Bot API access is a separate boundary
A server can also wrap Telegram's Bot API for bot-side operations. That is an access mechanism, not a guarantee of any one workflow above.
Telegram's Bots FAQ describes which messages bots receive, including how group privacy mode affects visibility. Its Bot API documentation also defines business connections with their own rights. Therefore, avoid both extremes: a bot token is not general access to your personal inbox, but bot-based business integrations should not be dismissed without checking their actual rights and supported workflow.
Ask whether the server acts as a user, a bot, or an authorized business bot, and which chats and operations that identity covers. For a broader product decision, see Telegram CRM versus bots versus shared inboxes.
Questions to answer before connecting
- Who maintains it? Check the repository owner or service provider. A Telegram-related name, use of an official API, or operation of Telegram Web does not establish that Telegram publishes or endorses the MCP server.
- Which identity is used? Record the intended account, bot, team, and environment privately. Do not paste session files, bot tokens, or login codes into an evaluation report.
- What can it actually retrieve? Check history ranges, pagination, archived-chat coverage, and whether results come from live Telegram or stored CRM data.
- What can change? Separate reads, stored previews, CRM edits, Telegram actions, and host-computer operations. Inspect enforced permissions and the client's prompting behavior.
- Where does returned content go? Follow the path from Telegram through the server to the AI client and its model provider. Running the adapter locally does not by itself keep model inputs local.
- How do you disconnect? Identify the relevant grant or session revocation process. Disconnecting future access does not retract content already returned to a client.
Workflow instructions are another layer. The Telegram Skills catalog provides task guidance, but instructions should not be mistaken for an enforced access boundary.
A small read-only acceptance exercise
Use one existing, non-sensitive conversation or test fixture that you are authorized to inspect. This is a proposed evaluation exercise, not a study with measured results.
First, state the job: “Read the last few messages in this permitted test conversation and report the latest explicit commitment. Do not send, mark read, sync, edit, or create a task.” Verify that the selected read tool does not perform those extra actions. If it does, choose a narrower operation or stop.
Then check four things:
- The returned identity and conversation match the intended scope.
- The result states its history range or pagination limit rather than implying complete coverage.
- The answer distinguishes an explicit commitment from an inference and points to supporting message context.
- No write was needed to obtain the result, and missing access is reported as a limitation rather than guessed content.
For a bot-testing adapter, use existing test messages without pressing buttons. For an agent remote, inspect existing control-channel messages without issuing execution commands. These exercises test different capabilities; do not score a tool as deficient for lacking a different architecture's purpose.
If customer context and follow-ups are your goal, start with the Chiho connection guide and run the bounded read check before expanding the workflow. Keep the result simple: intended job, verified access, observed limitations, and the next explicitly authorized action.